

- go-sample-frontend: the React front end, shared by all three sample apps.
- go-sample-backend-java: the Java backend.
- go-sample-backend-typescript: the TypeScript backend.
What this tutorial covers
By the end, you’ll have an account opening application that:- Starts a verification journey through the Go Journey API v2.
- Renders each screen from the journey’s own configuration, rather than from hardcoded forms.
- Collects identity details, contact details, an address, a photo ID, and a selfie.
- Screens the applicant against PEPs and sanctions lists.
- Polls for the outcome and shows the decision, including a referral to manual review.
This is the API sample app tutorial. It covers the API-first integration only, and does not cover the SDK or hosted journeys. For how the sample apps are built and what they share, see the Sample applications overview.
Prerequisites
- Access to the Go dashboard, with permission to create and publish journeys.
- Licences for the modules this tutorial uses. Licences are assigned to your department by GBG, and an unlicensed module shows a warning icon in the Journey builder.
- An API client. See Manage API clients for how to create one and get your client ID and secret.
- Node.js v18 or higher, for the front end and the TypeScript backend.
- JDK 21 and Maven, only if you choose the Java backend.
- Git, to clone the sample repositories.
Part 1: Build the journey
The application renders its screens from whatever your journey collects, so the journey comes first. An account opening journey does more than confirm who someone is. It also screens them against sanctions and PEPs lists, and it gives a reviewer a way to resolve the cases that sit between accept and reject. The finished journey looks like this. Eight modules run in sequence, then three evaluation nodes route the applicant to accept, reject, or a manual review that a person resolves.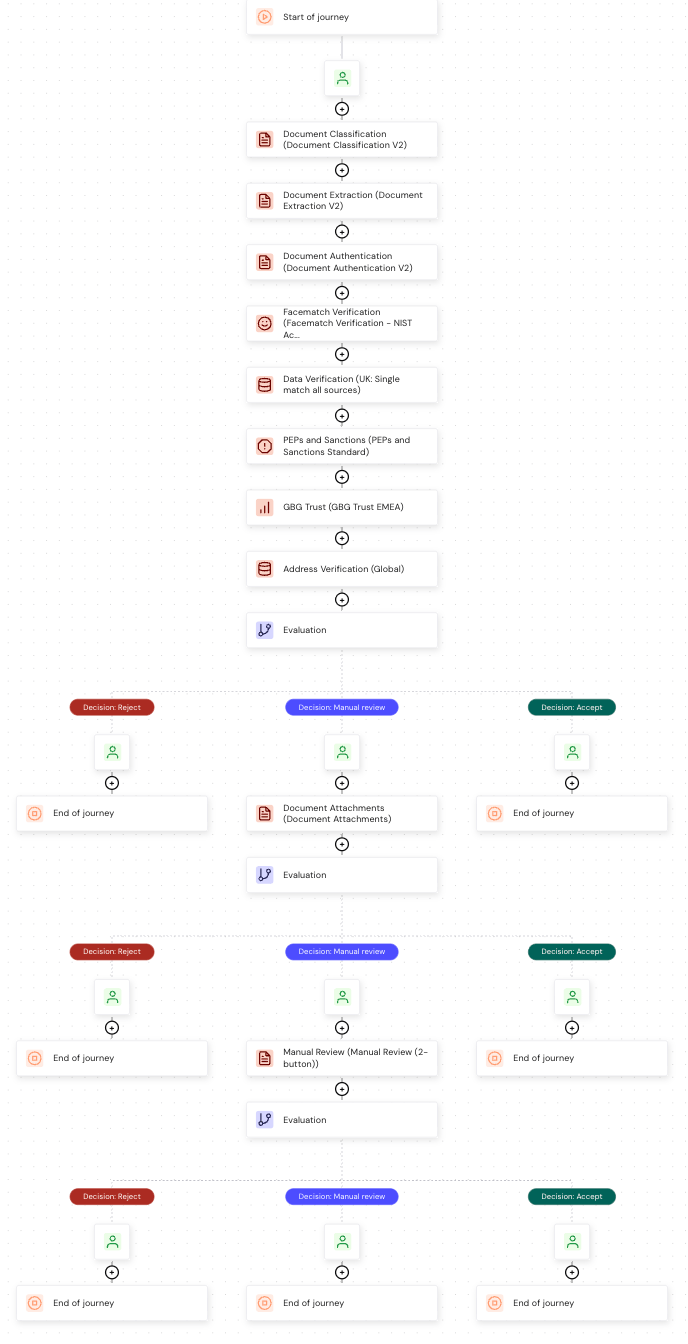
The banking account opening journey
1
Add the modules
In the Journey builder, add these modules in order:For instructions, see Configure modules.
Select the v2 variant of each document module, for example Document Classification v2 rather than Document Classification. The v2 variants are built for this API.
2
Set the country on Address Verification
Address Verification takes the country from its own settings rather than from the applicant’s address, so it needs setting before the journey runs.
- Click the Address Verification (Global) module in the journey.
- Click Settings.
- In the Country field, enter the ISO3 code for the country you verify addresses in, for example
GBR. - Click Save all settings.
ISO3 codes are the GO platform convention, so
GBR, FRA or DEU. An ISO2 code such as GB is also accepted. For US addresses, use the dedicated US variant instead, which is certified for USPS DPV and CASS.3
Set the dataset on PEPs and Sanctions
The module screens against whichever datasets its settings name. This tutorial uses Politically Exposed Persons only, so the evaluation has a single outcome to act on.
- Click the PEPs and Sanctions Standard module in the journey.
- Click Settings.
- Click the Datasets field and select Politically Exposed Persons. Remove any other dataset, so it’s the only one listed.
- Click Save all settings.
You can screen against sanctions lists too by adding that dataset here. If you do, the module can return a match from either list, so revisit the PEPs and Sanctions conditions in your evaluation.
4
Add the first evaluation
Add an Evaluation node after the modules and configure these three decisions. For how to add and configure one, see Set up evaluation.
Set the classification on each decision as shown. The application reads it to choose a result screen, where
positive renders an approval, negative a decline, and neutral a referral to manual review.Give the Reject and Accept branches an End of journey node.5
Add the manual review branch
The Manual review branch does not end the journey. It hands the case to a person.On that branch, add:
- A Document Attachments module, so the reviewer has the captured document to look at.
- A second Evaluation node with one decision, Manual review with classification Neutral and All Match, where Document Attachments is ATTACHED.
- A Manual Review module on that branch, configured as a two-button review.
6
Add the review outcome evaluation
Add a final Evaluation node after the Manual Review module, to turn the reviewer’s answer into a decision:
Give each branch an End of journey node.A Timeout stays neutral because nobody decided. The applicant sees the same referral screen as before.
7
Publish to Preview
Click Publish to Preview. You’ll see the confirmation message Delivery deployed successfully.Use Preview while you build and test. Publish to Production when you’re ready for real applicants. The application works the same against either, and only the resource ID changes.
8
Copy the resource ID and version
Go to Dashboard in the Journey builder and copy the Resource ID and Version number.You’ll combine them as
<resourceId>@<version>, for example:Part 2: Set up the backend
Clone the backend in the language you prefer. Both expose the same HTTP API, so the front end works with either.- Java
- TypeScript
.env.local in the repository root:src/main/resources/application-northbank.yml and set your journey:http://localhost:8081. The script finds JDK 21, loads .env.local, and starts the right profile.live command is what switches them to your real journey.
Set your region
The samples default to the EU platform. If your tenant was provisioned elsewhere, then change the base URL and the region together:- Java
- TypeScript
In
application-northbank.yml:Part 3: Set up the front end
The front end is one repository holding three applications. This tutorial uses the banking one.apps/northbank/.env.local:
NEXT_PUBLIC_* values are compiled into the browser bundle. Never put credentials here. They belong in the backend’s .env.local.http://localhost:3000. With the backend already running, you’ll land on the first screen of your own journey.
If you see the About you screen, the whole chain is working, from the browser through the front end and backend to GBG Go.
Troubleshooting
The document screen is skipped
The document screen is skipped
On this journey the document element sits under an optional parent, so its refs never appear in
outstanding. The sample marks that screen always-collect in the Java config, or alwaysCollect in TypeScript, so it renders from collects regardless.If you build your own screen plan and the document screen never appears, this is why.The app shows a generic 'A few more details' form
The app shows a generic 'A few more details' form
The screen plan doesn’t recognise something the journey collects, so the app falls back to a plain form rather than stalling.This usually means the journey changed after the plan was written. Check the backend log for
No screen mapped for outstanding elements, which names the unmapped elements, then add them to the screen plan.A screen asks for details the customer already entered
A screen asks for details the customer already entered
The journey’s required fields changed under the same resource ID. A republish can add required elements, so an address that needed three components can come back needing six, and a screen plan written against the old shape submits an incomplete element.Re-read
collects after every republish rather than assuming the shape holds.Every request fails with an expired session
Every request fails with an expired session
The backend keeps sessions in memory, so restarting it invalidates every session in progress. Start a new journey.For the same reason, the samples run one journey per browser tab. The session ID lives in
sessionStorage, so reloading resumes the journey, but a new tab starts a fresh one.Authentication succeeds but journey calls fail
Authentication succeeds but journey calls fail
The region is mismatched. The token endpoint is global, so authentication works regardless, but journey calls go to a regional host. Check that
region and base-url name the same region.A module returns an error rather than a decision
A module returns an error rather than a decision
A module that errors is different from one that declines, because nothing was decided about the customer.Open the journey in the Investigation portal and look at the failing step. It carries an error code, a problem description, a suggested action, and a correlation ID. Quote the correlation ID when contacting support, because it identifies the exact execution.
Next steps
Review the outcome
See the journeys you ran, module by module, in the Investigation portal.
Configure outcomes
Change what each module reports, and how your evaluation turns those into decisions.
Publish to Production
Move from Preview to Production when you’re ready for real customers.
Explore the API
The full Journey API v2 reference.